Select model
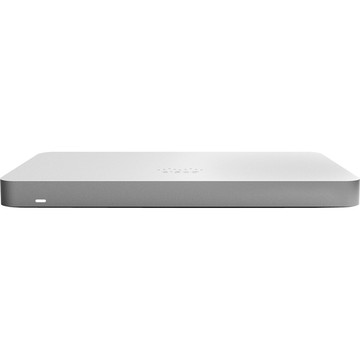
The Cisco Meraki MX67 is a cloud-managed network security and firewall appliance designed for organizations that need Unified Threat Management across distributed sites, campuses, or datacenter VPN concentration. Its 100% cloud-managed architecture means network administrators can deploy, configure, and monitor the device remotely through a web-based dashboard without on-site intervention. The appliance consolidates SD-WAN, application-aware firewalling, content filtering, intrusion prevention, and advanced malware protection into a single desktop unit that also supports wall mounting.
Key Features:
- Five 10/100/1000Base-T Gigabit Ethernet RJ-45 ports deliver flexible, high-speed connectivity for branch and small-site deployments.
- Cloud management through the Meraki dashboard unifies firewall policy, switching, wireless LAN, and mobile device management in a single interface, eliminating the need to manage separate platforms.
- Auto VPN with IKE/IPsec generates VPN routes automatically and can run on the physical appliance or as a virtual instance in Amazon AWS or Microsoft Azure, simplifying multi-site connectivity.
- SD-WAN with active/active VPN, policy-based routing, and dynamic path selection allows traffic to be steered intelligently across available WAN links based on application-layer performance profiles.
- A SNORT-based intrusion prevention system drawing on Cisco's signature database provides PCI-compliant IPS sensing, while Cisco AMP adds file reputation-based malware protection.
- Content filtering covers CIPA-compliant web filtering, safe-search enforcement for Google and Bing, and YouTube for Schools controls, giving administrators granular control over user browsing.
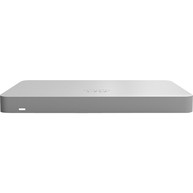
- Desktop and wall-mountable form factor measuring 9.4" wide, 5.1" deep, and 1.1" tall, weighing 1.74 lb, makes the unit practical for space-constrained branch locations.
- A lifetime limited warranty and RoHS environmental compliance reflect long-term supportability and responsible materials sourcing.
A Consolidated Branch Security Platform
The MX67 sits within Cisco Meraki's MX family as an appliance aimed at smaller distributed sites that still require enterprise-grade threat management. Rather than deploying separate boxes for firewalling, WAN optimization, and VPN, the MX67 brings those capabilities together under a single cloud-managed umbrella, reducing both hardware footprint and administrative overhead.
Cloud Management That Scales With the Deployment
Because the MX67 is 100% cloud managed, every configuration change made through the Meraki dashboard propagates without requiring a technician at the remote site. Template-based settings allow administrators to push consistent policies from small deployments to tens of thousands of devices using the same workflow. Role-based administration, configurable email alerts, and auditable change logs give IT teams clear visibility and control regardless of deployment size. Summary reports archive user, device, and application usage details in the cloud for ongoing review.
Unified Threat Management Capabilities
The appliance supports threat protection, stateful packet filtering, application control, identity-based policies, web content filtering, intrusion prevention, malware protection, and VPN failover from a single platform. Application-aware traffic control operates at Layer 7, meaning administrators can set bandwidth policies by application type rather than just by port or protocol. Identity-based security policies extend access control to the user level rather than relying solely on IP address.
Intrusion Prevention and Malware Protection
The integrated IPS sensor uses the SNORT signature database maintained by Cisco, providing a PCI-compliant detection and prevention capability that updates through the cloud without manual signature management. Cisco AMP adds a file reputation layer that evaluates files against a continuously updated threat intelligence database, catching malware that signature-only approaches may miss.
Site-to-Site and Client VPN
Auto VPN generates the necessary IKE/IPsec routes automatically when appliances are enrolled in the same Meraki organization, making multi-site VPN mesh a configuration task rather than an engineering project. The system interoperates with all IPsec VPN devices and services, so existing infrastructure does not need to be replaced. Automated failover from MPLS to VPN activates within seconds of a connection failure. For remote workers, client VPN uses L2TP IPsec and is natively supported on Windows, Mac OS X, iPad, and Android without per-user licensing fees.
SD-WAN and Path Intelligence
SD-WAN functionality runs alongside Auto VPN, supporting active/active VPN configurations, policy-based routing, and dynamic VPN path selection. Application-layer performance profiles let administrators define which application types receive prioritized routing, so latency-sensitive traffic is steered to the best available path rather than following static routing rules.
Branch Gateway Services Built In
The MX67 includes DHCP, NAT, QoS, and VLAN management so a branch site requires no additional gateway hardware for these functions. Web caching accelerates access to frequently requested content, reducing repeated WAN retrieval. Load balancing combines multiple WAN links into a single interface with configurable QoS, traffic shaping, and failover policies. Smart connection monitoring detects Layer 2 and Layer 3 outages automatically and triggers fast failover, with the option of an integrated LTE Advanced or 3G/4G modem for cellular backup.
Connectivity and Physical Design
Five Gigabit Ethernet RJ-45 ports operating at 10/100/1000Base-T handle all network connections, supplemented by a USB port for supported peripheral or management functions. The compact enclosure measures 9.4" x 5.1" x 1.1" and weighs 1.74 lb, deployable as a desktop unit or wall-mounted using the included mounting kit. The package also includes two Cat 5 Ethernet cables and an AC power adapter.
Environmental Compliance and Warranty
The MX67 carries Restriction of Hazardous Substances (RoHS) compliance, confirming that the appliance meets restrictions on hazardous materials in its construction. A lifetime limited warranty backs the hardware.
Cisco Meraki MX68 Gigabit Ethernet Firewall Appliance - MX68-HW
MX68-HW